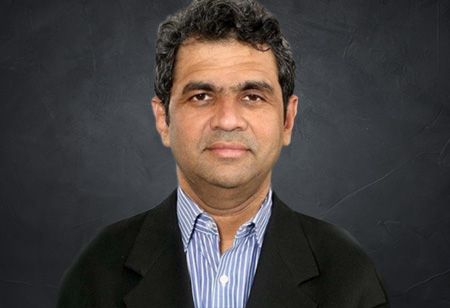
Abdul Azam, Founder & CEO, Akatalyst Technologies
In an exclusive interaction with Zeenat Parween, Sr. Correspondent at India Pharma Outlook, Abdullah Azam, Founder and CEO, Akatalyst Technologies, discusses the growing role of AI in pharmaceutical quality management, its potential to strengthen quality systems, and the challenges of adopting AI in regulated environments. He highlights how AI can support deviation management, CAPA, risk-based decision-making and audit preparation while maintaining regulatory compliance and patient safety.
With more than 25 years of experience in GxP quality, regulatory compliance and digital transformation, Abdullah Azam has held senior leadership positions at BioClinica and Clarivate. His expertise spans quality management systems, pharmacovigilance quality assurance, regulatory audits, computerized system validation and risk management. A Lean Six Sigma Master Black Belt and ISO & ISMS Lead Auditor, he focuses on strengthening quality systems through practical, risk-based approaches and technology-driven solutions.
AI is gaining attention in pharmaceutical quality management, but its adoption also raises concerns about reliability, transparency, and regulatory compliance. What are the biggest opportunities AI offers in pharma quality today, and what limitations should companies understand before adopting it?
I believe AI offers the opportunity to move pharmaceutical quality management towards a more proactive, connected and data-driven approach. Quality organization s generate significant amounts of information through deviations, CAPAs, audit observations, change controls, supplier assessments, complaints, and manufacturing records. However, these records are often reviewed and managed within individual processes, making it difficult to identify relationships and patterns across the wider quality system.
AI can help connect these information sources, identify recurring patterns, highlight potential systemic weaknesses, and support better-informed quality decisions. For example, a series of seemingly unrelated deviations may have a common underlying relationship with a particular supplier, equipment type, process or training gap.
Its greatest opportunity may therefore lie in helping organizations understand what individual quality events collectively reveal about the effectiveness of their quality management systems.
However, organizations must recognise that AI is only as useful as the quality and relevance of the information it works with. Incomplete, inconsistent or poorly structured data can produce misleading insights. AI can also generate plausible but incorrect explanations, overlook important context or identify correlations that don't establish causation. A pattern identified by AI isn't necessarily a root cause.
Before adoption, companies must clearly define the intended use, assess the suitability of the technology and underlying data, establish appropriate controls and evaluate the reliability of outputs. Human oversight is essential, particularly where outputs influence decisions affecting product quality, compliance or patient safety.
AI should strengthen the quality management system and the judgement of quality professionals. It shouldn't replace scientific thinking, professional accountability or established quality principles, and it shouldn't become another technology layer that adds complexity without delivering measurable value.
Many life sciences companies are exploring AI for deviation management, CAPA, change control, and audit preparation. Which quality processes offer the strongest opportunities for AI adoption, and where should companies begin?
Deviation management and CAPA offer some of the strongest opportunities because they involve large volumes of historical information, investigation activities and decisions that can benefit from better analysis.
AI can help investigators retrieve similar historical events, identify recurring patterns, organise relevant evidence and explore possible relationships with equipment, suppliers, processes, environmental conditions or training.
CAPA effectiveness is another important area. Organization s sometimes focus heavily on closing corrective and preventive actions within prescribed timelines. However, timely closure doesn't necessarily mean that the underlying problem has been resolved. AI can help identify recurrence patterns after CAPA implementation and provide insights into whether similar events continue to occur.
Change control can also benefit. When a process, equipment item, supplier or system changes, AI could help retrieve related procedures, validation documents, training requirements and historical changes, although the final impact assessment must remain a controlled quality decision.
In audit preparation, AI can retrieve relevant evidence, flag potential documentation gaps and highlight recurring observations, so quality teams can spend more time evaluating the adequacy of controls.
I would recommend that companies begin with a genuine quality problem and a clearly defined, bounded use case where AI assists rather than independently makes quality decisions. They should establish baseline performance, evaluate the reliability of outputs and measure whether the application improves investigation quality, reduces processing time or strengthens process effectiveness.
Also Read: Why Clinical Evidence Matters More in MedTech Commercialization
AI can help identify potential compliance risks, but not every flagged issue requires the same level of attention. How can quality leaders use risk-based AI insights to prioritise deviations, CAPAs, and audit findings without overlooking issues that could affect product quality or patient safety?
In my view, AI should operate within an established Quality Risk Management framework, aligned with the principles of ICH Q9(R1). Prioritisation must be based on scientific knowledge, process understanding and an assessment of potential impact on product quality and patient safety.
AI can connect information across quality processes. A deviation, a supplier audit observation, a complaint and a recurring CAPA may look like separate events when reviewed individually, yet together indicate a common risk or an emerging systemic weakness. AI can help quality leaders recognise such relationships and direct attention to them.
However, an AI-generated risk score or alert should never be treated as the final risk assessment. A recurring minor documentation issue and an isolated event with potentially serious implications for patient safety require different considerations. Risk decisions must account for factors such as severity, occurrence, detectability, existing controls, process context and the potential consequences of failure.
Organizations should establish clear escalation criteria and define which decisions require review and approval by qualified personnel. The rationale for prioritisation should also be documented so that decisions remain transparent and traceable. This is particularly important when AI recommendations influence the handling of deviations, CAPAs, or other regulated quality records.
Another important consideration is the possibility of both false positives and false negatives. Excessive alerts can create alert fatigue, while missed signals can result in significant risks being overlooked. AI models and their outputs must therefore be evaluated periodically, and risk assessments should be revisited as new information becomes available.
The objective isn't to let AI decide which quality issues matter. It's to help quality professionals identify potential risks earlier, understand relationships across the quality system and allocate attention and resources more effectively.
Traditional CSV approaches can be documentation-heavy. How can risk-based approaches such as CSA help life sciences companies validate AI-enabled systems more efficiently without weakening compliance controls?
The opportunity is to move from a predominantly documentation-driven approach towards evidence-based assurance that is proportionate to the intended use and risk of the system. This doesn't mean eliminating validation or reducing testing indiscriminately. It means focusing assurance activities on the functions, failure modes and behaviours that could affect product quality, patient safety, data integrity or regulatory compliance.
For AI-enabled systems, organization s must assess the intended use, suitability and integrity of the underlying data, reliability and limitations of model outputs, and the consequences of incorrect recommendations. The level of assurance should reflect how the system is used. An AI application that retrieves controlled documents presents a different risk from one that recommends root causes, prioritises quality events or influences a critical quality decision.
Testing should include representative and challenging scenarios, including incomplete, inaccurate or unexpected inputs. Organization s must also address model updates, version control, performance monitoring and periodic reassessment. AI systems can change in behaviour as models, configurations or underlying data change, so assurance can't be treated as a one-time activity.
An equally important distinction is between demonstrating that the technology functions as intended and demonstrating that the business process using it is effective and compliant. Both require appropriate oversight. A technically functioning AI application doesn't automatically establish that an investigation is adequate, a CAPA is effective, or a quality decision is scientifically justified.
Computer Software Assurance (CSA) is FDA's risk-based assurance approach for production and quality system software in the medical-device sector. For pharmaceutical manufacturers, the relevant framework includes EU GMP Annex 11 for computerised systems, supported by industry guidance such as GAMP 5. ISPE has also published specific guidance on AI-enabled GxP systems. The EU's proposed Annex 22 on AI is still in draft, and its approach to dynamic and generative models is still evolving, so organizations should apply risk-based assurance within the requirements of their applicable framework and keep pace with evolving guidance.
The objective is more targeted assurance, supported by objective evidence, rather than simply more documentation.
Also Read: How Deviation Trends Can Reveal Hidden Pharma Quality Risks
Smaller pharma, biotech, MedTech, and healthtech companies may lack dedicated validation and compliance teams. How can these organization s adopt AI-driven quality systems without unnecessary costs or compliance risks they cannot manage?
Smaller organizations don't necessarily need large technology or validation teams to benefit from AI. However, they do need a sound quality management foundation. This includes clearly defined processes, responsibilities, reliable records, and consistent management of quality events. Introducing AI into fragmented processes or poor-quality data may simply reproduce existing weaknesses at a faster rate.
A pragmatic approach is to begin with practical applications that offer value without immediately placing AI in critical quality decision-making. Examples include searching controlled documents, retrieving historical quality records, supporting audit preparation, identifying trends, and assisting with the organization of investigation evidence. These applications can improve efficiency while allowing the organization to develop an understanding of the technology and its limitations.
Organizations should also evaluate whether the technology is appropriate for their operating environment. Important considerations include data protection, access controls, audit trails, record retention, system integration, supplier oversight, and how model updates are managed. They should understand where their data is stored, who can access it, and whether their information may be used to train external models.
Where AI outputs or decisions based on them form part of GxP records, appropriate controls for electronic records, audit trails and data integrity must be maintained in line with applicable requirements such as 21 CFR Part 11 and EU GMP Annex 11. The intended use of the application and its role in regulated activities should determine the level of assurance and governance required.
The assurance effort should be proportionate to the intended use and risk, but regulatory responsibilities don't disappear because an organization is small. Vendor qualification, appropriate procedures, user training and external specialist support can help bridge internal capability gaps. Organizations should also consider the total cost of ownership, including implementation, assurance, governance, training, maintenance, and ongoing monitoring, rather than looking only at the initial subscription or licence cost.
Based on your experience, what is one key piece of advice for life sciences and healthtech organizations adopting AI to balance innovation with quality, regulatory compliance, and patient safety?
My key advice is to begin with a clearly defined quality problem and a well-understood intended use for the AI application, rather than adopting the technology simply because it is available.
Organizations must understand the decisions an AI system may influence, the consequences of incorrect outputs, and the level of human oversight required. Accountability for quality, regulatory compliance and patient safety must remain with the organization and its qualified personnel.
The true measure of an effective quality system is not how well it documents what went wrong, but how effectively it helps an organization prevent problems from recurring and protect patients. AI should help us move closer to that objective.

, CDSCO.jpg "Fostering a Quality Culture in the Pharmaceutical Industry")